


One secure network for every location
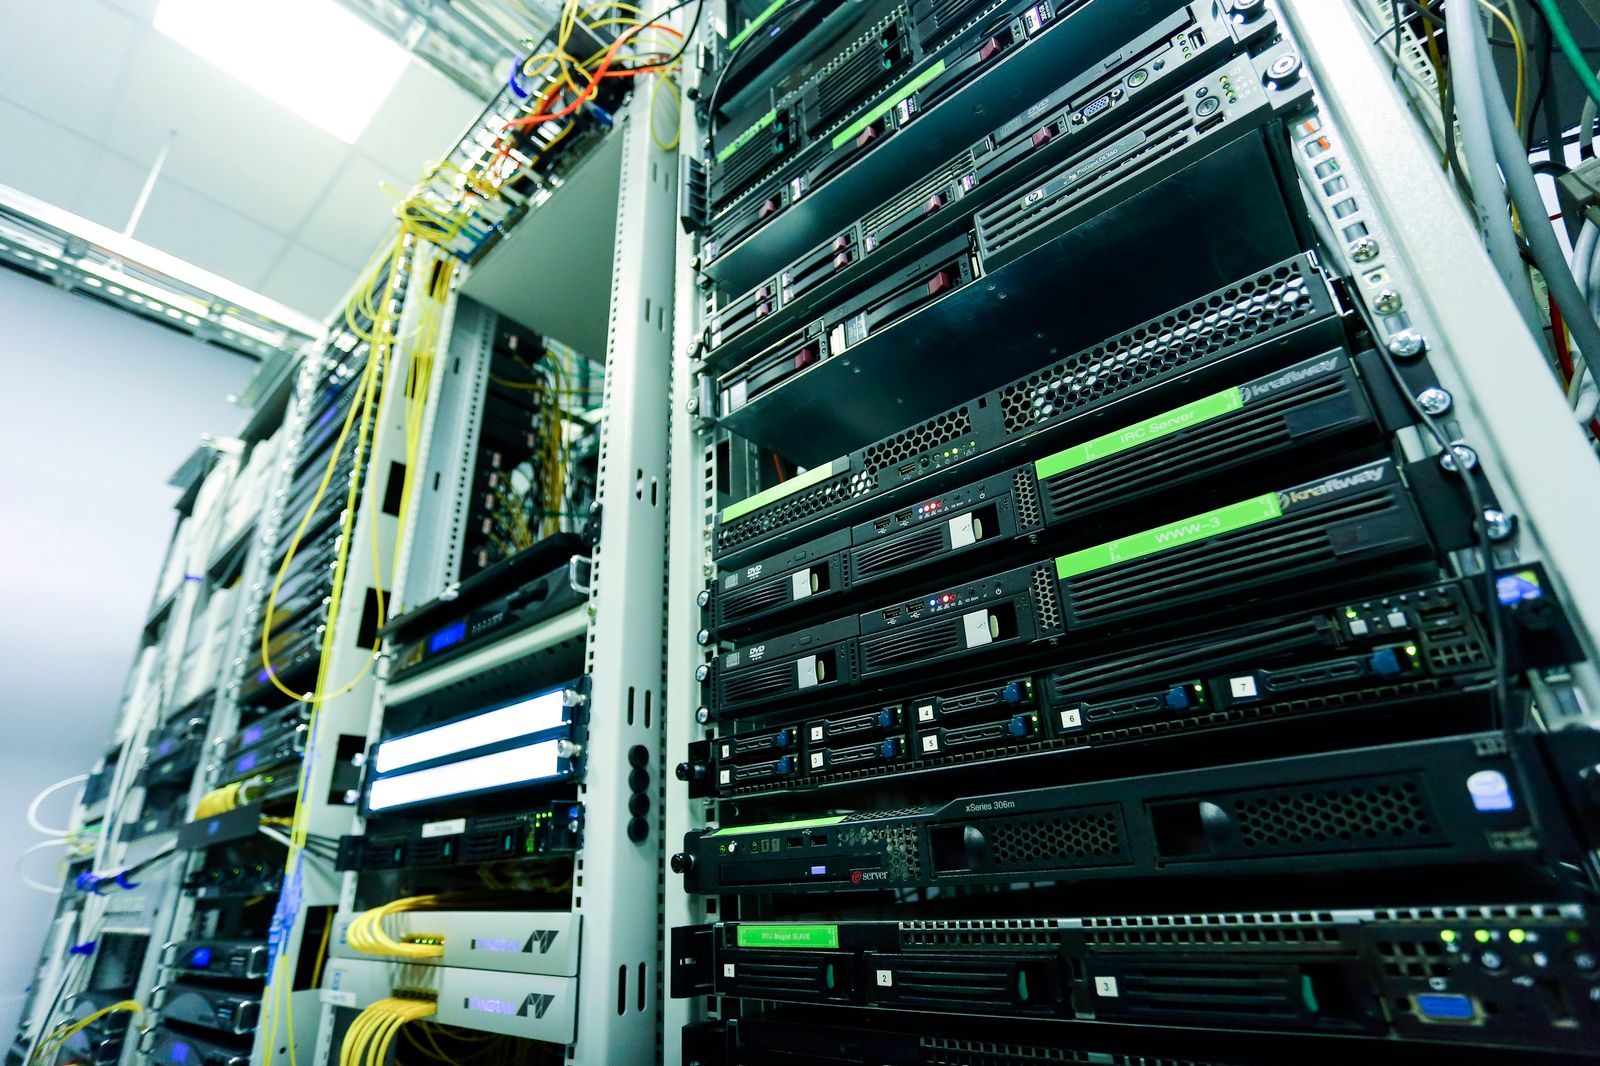
When your business runs on cloud apps, VoIP and video, the network between your offices matters as much as the computers in them. Traditional site-to-site VPNs and MPLS lines are slow to change, expensive and often have a single point of failure. SD-WAN replaces them with an intelligent overlay that uses multiple internet connections at each site, picks the best path for every application in real time and fails over automatically.
CAL IT Group builds SD-WAN on the platform that fits your business — Cisco Meraki, Fortinet or SonicWall — so every site, from your headquarters to a two-person branch, gets the same security, the same policies and the same visibility, all managed from one dashboard by our 24×7 Network Operations Center.
What every SD-WAN site gets
- Security & SD-WAN
A next-generation firewall at every site
Firewall, intrusion prevention, content filtering and SD-WAN in one appliance at every location, sized from small branches to large headquarters and data centers.
Meraki MX · FortiGate · SonicWall - Site-to-site
Encrypted site-to-site VPN
Encrypted tunnels link every location and are maintained automatically — add a new site and it joins the network quickly, with policies applied from the central console.
Mesh or hub-and-spoke - Performance
Intelligent path selection
Dual uplinks with performance-based routing send voice, video and critical apps over the healthiest connection, measured continuously for latency, jitter and loss.
SD-WAN policies - Backup
A backup that fits the location
Each site gets a primary connection and a backup appropriate for the location — coax, fixed wireless, or a cellular gateway or built-in LTE/5G — so a cut fiber line doesn’t stop the business.
Primary + backup per site - LAN
Switching & Wi-Fi
Switches and access points from the same platform extend the same policies from the WAN to every port and wireless network, managed from the same console.
Switches & access points - Visibility
One cloud dashboard
Real-time health, application usage and alerts for every site in one place — so our NOC sees problems first and you get clear reporting.
One console for every site - Remote users
Secure remote access
Client VPN or zero-trust access extends the same protection to people working from home or on the road.
Client VPN · zero-trust access - Security
Layered with our security stack
Cisco Umbrella DNS filtering, SentinelOne on every device and our 24×7 SOC work alongside the firewall at every site.
Defense in depth
Why businesses move to SD-WAN
- Stay online. A primary and a backup connection per site with automatic failover — no single circuit can take a location down.
- Better calls and cloud apps. Voice, Microsoft 365, ERP and video get priority on the best-performing path.
- Lower circuit costs. Business broadband and fiber replace expensive MPLS lines without giving up performance or security.
- New sites in days. Pre-configured hardware ships to the location, plugs in and joins the network — ideal for growing companies, warehouses and pop-up sites.
- Consistent security. One set of firewall, filtering and access policies applied at every location from a single dashboard.
Designed, deployed and managed by one local team
- Assess and design. We review your locations, circuits, applications and current firewalls, then design the SD-WAN topology, recommend the right platform and models, and choose primary and backup carriers for each site through our connectivity consulting.
- Stage and deploy. Hardware is configured and tested in our Huntington Beach office before it ships. Sites cut over on a schedule you approve, as a fixed-fee project.
- Monitor and manage. Our 24×7 NOC watches every appliance and circuit, handles firmware, policy changes and carrier tickets, and our network engineers document everything to standard.
Plan your SD-WAN All cloud services
Cisco, Meraki and Umbrella are trademarks of Cisco Systems, Inc. Fortinet and FortiGate are trademarks of Fortinet, Inc. SonicWall is a trademark of SonicWall Inc. SentinelOne is a trademark of its owner.