

5.0 on Google & Clutch 96%LIVE of calls answered in under 60 seconds by our local Huntington Beach team

SOC 2 Readiness for Orange County Companies

When customers start asking for a SOC 2 report, you need more than a template. CAL IT Group holds SOC 2 Type II across all five Trust Services Criteria, so we know what auditors look for — and we get you ready for yours: scope, gaps, controls, policies and the evidence that proves them.

96%LIVE of calls answered in under 60 seconds by our local Huntington Beach team 24×7 NOC & SOC monitoring SOC 2 Type II all five Trust Services Criteria On-site support, included 5.0 on Google & Clutch

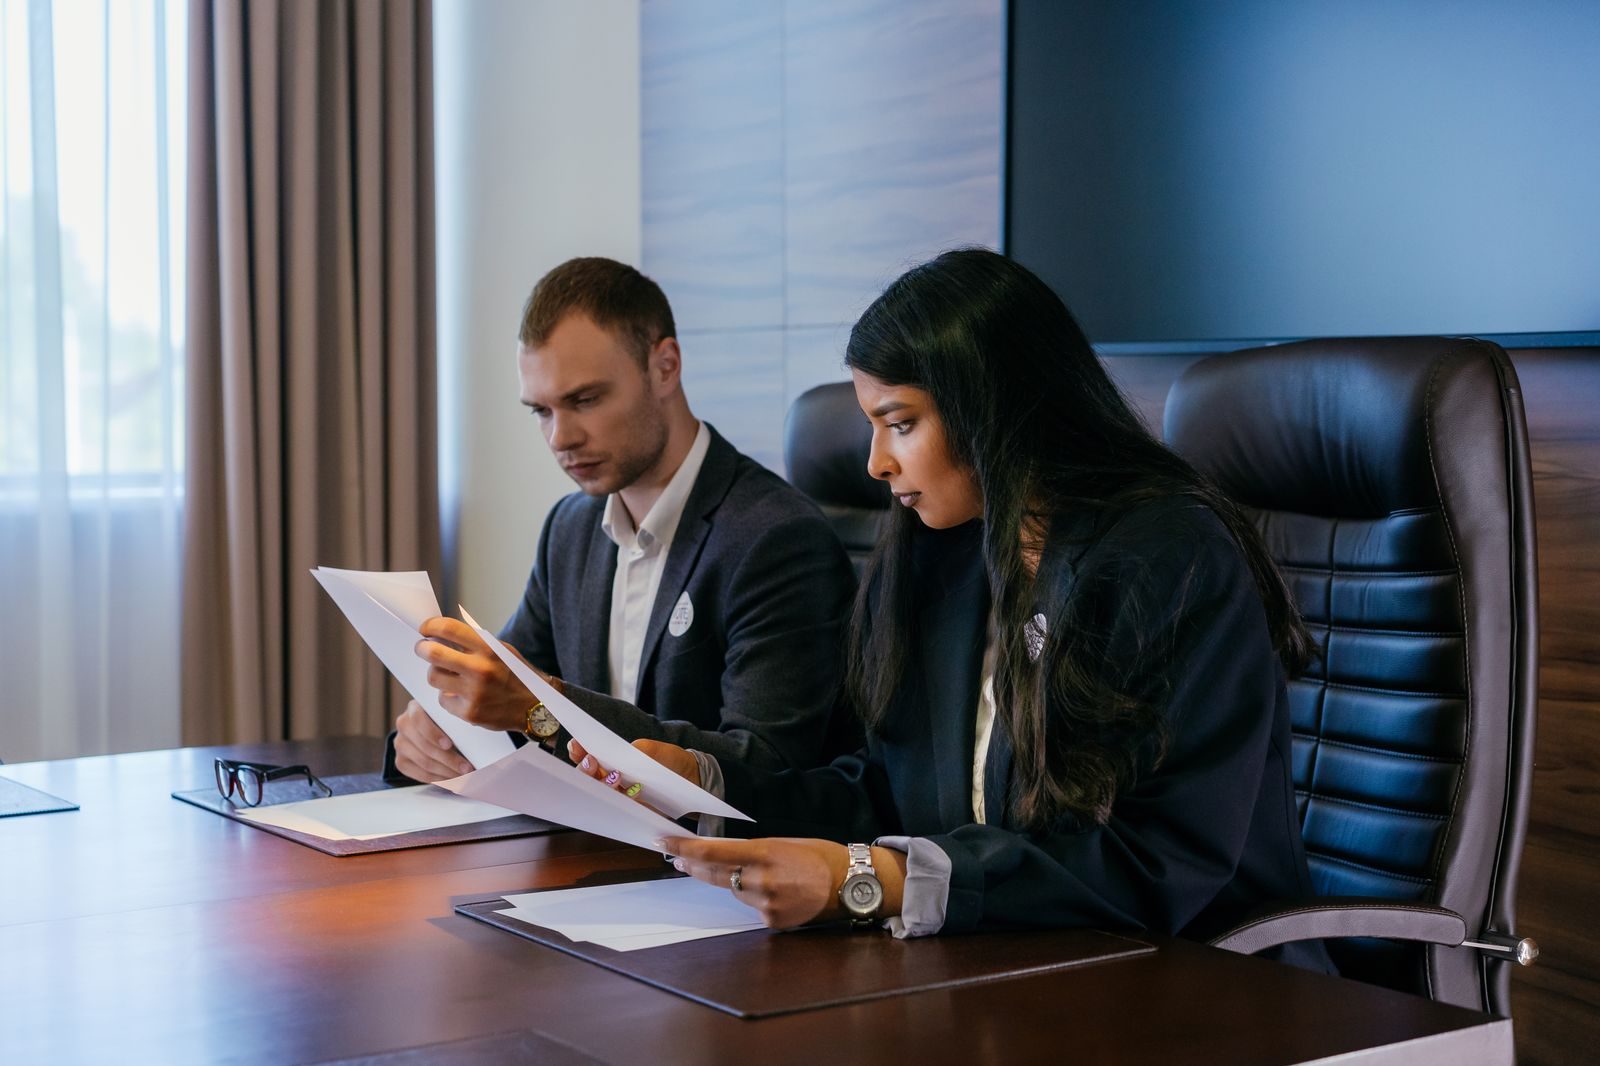
Two professionals reviewing audit documents at a conference table

SOC 2 readiness · all five criteria

Audit-ready, criterion by criterion.

We’ve been through a SOC 2 Type II audit across all five Trust Services Criteria ourselves. We take you down the same path — scope, gap assessment, controls, policies and evidence — until you’re ready for your auditor.

  • Scope set to what you promise your customers
  • Every gap ranked by risk and effort
  • Controls, policies and evidence put in place
  • Support through fieldwork and the observation period
Ready for a SOC 2 audit, criterion by criterion The five Trust Services Criteria — Security, Availability, Processing integrity, Confidentiality and Privacy — each brought to ready and checked off, with evidence collected all year, until you are ready for your auditor. Trust Services CriteriaSecurity first, plus the ones you promise customers Security Availability Processing integrity Confidentiality Privacy Evidence collected all year Ready for your auditor ✓

Technology partners

The platforms behind SOC 2 Readiness

See our partners →
  • Vanta logo
  • Microsoft logo
  • Cisco Duo logo
  • SentinelOne logo
  • Silverfort logo

Built by a team that’s been through it

We didn’t learn SOC 2 from a slide deck. CAL IT Group completed a SOC 2 Type II audit across all five Trust Services Criteria — Security, Availability, Processing Integrity, Confidentiality and Privacy — so we’ve built the controls, written the policies and answered the auditor’s requests ourselves. Read about our own SOC 2 Type II.

Our path to audit-ready

  • 01 · Scope

    Decide what’s in scope

    The systems, data and people the report covers, and the Trust Services Criteria that match what you promise customers.

    Scope document
  • 02 · Assess

    Gap assessment

    Your environment and practices measured against the criteria, with every gap ranked by risk and effort.

    Gap report
  • 03 · Implement

    Put the controls in place

    MFA and conditional access, endpoint detection and response, logging and monitoring, backups, vulnerability management, access reviews and change management.

    Microsoft 365 · Intune
  • 04 · Document

    Policies and procedures

    An information security policy set written for how your company actually works, approved by leadership and acknowledged by staff.

    Policy set
  • 05 · Evidence

    Collect the proof

    Evidence gathered continuously — automated where a compliance platform can do it, organized for the auditor where it can’t.

    Compliance platform
  • 06 · Audit

    Support through the audit

    A readiness review before the auditor arrives, help choosing an audit firm, and answers to their requests during fieldwork and the observation period.

    Auditor requests

Much of SOC 2 is already part of Managed Care

Many of the technical controls auditors test are things Managed Care already runs for you every day:

That leaves the parts only you can own — your policies, your risk decisions and your vendor reviews — and your vCISO guides you through those.

Other frameworks

The same approach works for the other frameworks Orange County companies answer to: CMMC and NIST 800-171 for defense suppliers, and PCI DSS and customer security questionnaires through our security and compliance services.

Talk to us about SOC 2 SOC 2 Type II explained

What sets us apart

Fast response, deep security, senior expertise and engineers on-site.

<60 sec to a live engineer

Response time you can measure

96%LIVE of calls are answered by an engineer in under 60 seconds, every ticket is assigned in under 10 minutes, and every email or portal ticket gets a real engineer within 20 minutes (Mon–Fri, 5 AM–6 PM). Calls never go to voicemail during service desk hours, and the same team is on call 24×7.

See the live numbers →

24×7 NOC & SOC MSSP-grade security

A security provider, not just an IT provider

We operate as a managed security service provider (MSSP): SentinelOne MxDR, a 24×7 NOC & SOC, managed SIEM, DefensX browser security, security awareness training, vulnerability management, penetration testing and CMMC support — run by a team audited for SOC 2 Type II across all five Trust Services Criteria.

Our security services →

55+ years of combined experience

Senior technical expertise behind every ticket

Led by hands-on co-founders Kevin Nichols and Joe Kemp, with 55+ years of combined IT experience. Every engineer passes a technical assessment, we staff above our workload, and nobody works on something they’ve never seen before without an experienced engineer alongside — no call center, no offshore tier.

Meet the founders →

On-site included, no trip fees

Engineers who come to you

When hands-on work is needed, a local engineer is dispatched from our Huntington Beach office. On-site support is included in Managed Care — no dispatch fees, trip charges or hourly on-site rates — from the same team that knows your environment.

Areas we serve →

We re-earn your business on every ticket. No contract ever replaces doing the work well. Every user who opens a ticket gets a satisfaction survey when it closes, and every score is visible to our whole team and leadership — the averages are published live for anyone to see.

See our survey results →

Best-of-breed, by design

Industry-leading tools, chosen and run by engineers

We’re technology agnostic: we don’t resell a single vendor’s bundle or push the platform with the best margin. Every tool we recommend is a best-of-breed industry leader — selected, tested and configured by our own engineers because it’s right for your business.

Our leadership team is highly technical. Our co-founders, Kevin Nichols and Joe Kemp, are hands-on engineers, not just managers, and they constantly re-evaluate our tools and service offering — retiring what falls behind and adding what keeps clients ahead. You get enterprise-class technology that keeps improving, without lifting a finger.

  • SentinelOneMxDR endpoint protection
  • Microsoft DefenderPlan 2 & Intune device management
  • QualysVulnerability management
  • LiongardConfiguration & change monitoring
  • NinjaOneRemote monitoring & patching
  • 24×7 NOC & SOCManaged SIEM & threat hunting
  • Veeam + AzureBackup & off-site replication
  • Azure Site RecoveryCloud disaster recovery

Just some of the technologies we use.

SOC 2 Readiness FAQs

Do you issue SOC 2 reports?

No. SOC 2 reports are issued by licensed CPA firms. We prepare you for the audit — scoping, controls, policies and evidence — and support you while the auditor does their work.

What’s the difference between SOC 2 Type I and Type II?

A Type I report looks at whether your controls are designed properly at a single point in time. A Type II report tests whether they actually worked over a period, often 3 to 12 months. Most customers ask for Type II.

Which Trust Services Criteria do we need?

Security is required in every SOC 2. Availability, Confidentiality, Processing Integrity and Privacy are added based on what you promise your customers. We help you choose — CAL IT Group itself is audited for all five.

How long does it take to get ready?

It depends on where you start. Companies already on Managed Care usually have many of the technical controls in place; the remaining work is mostly policies, procedures and evidence. A Type II report then needs its observation period.

Is SOC 2 readiness included in Managed Care?

The security controls and your vCISO’s guidance are included in Managed Care. The readiness project itself — scoping, policies, evidence setup and audit support — is quoted as a fixed fee for Managed Care clients.

Success stories

Rated 5.0 on Google and Clutch.

Real reviews from the businesses we support — not a curated quote wall.

★★★★★Google
“Knowledgeable and proactive group that partners with you to assure your objectives are met, along with planning for future needs. All balanced with supporting your business day in and day out with a friendly, responsive and competent help desk. Recommend and would select them again!”
Tom G
★★★★★Google
“CAL IT has been a game changer for us. They tackle issues quickly and efficiently for us. So grateful their expertise. I highly recommend their services.”
Kelli Foudy
★★★★★Google
“We have worked with Cal It for several years now, They are very responsive and professional. We would highly recommend them.”
Cathy Goff

Customer service first · we re-earn your business on every ticket

Obsessive about service. Relentless about the details.

CAL IT Group brings enterprise-class IT, cybersecurity and SOC 2 Type II–audited operational excellence to small and midsize businesses across Southern California — a customer service organization first and foremost, proven day in and day out for over 10 years.

Call 866.24.CALIT