

MDR and SOC as a service, explained
Antivirus waits for something it recognizes. Managed detection and response (MDR) watches for behavior — a process encrypting files, a login from a new country, a tool attackers use — and puts people behind the alerts who can act at 2 AM. SOC as a service gives you those people: a 24×7 security operations center you’d otherwise have to staff yourself, at a cost few small and mid-sized businesses can justify.
Our service combines both, powered by SentinelOne and extended across email, Microsoft 365, cloud and network logs — what the industry calls XDR. When a threat is found, it’s contained on the spot: the device is isolated, the process stopped and, where ransomware has touched files, changes rolled back.
Detect
Behavioral AI on every managed laptop, desktop and server, plus security logs from firewalls, Microsoft 365, Azure, AWS and Google Workspace in a managed SIEM.
Respond
Automated containment within the agent, then analysts in our 24×7 SOC investigate, remediate and tell you what happened.
Recover
Rollback of ransomware changes where possible, clean-up of compromised accounts, and our breach response team if an incident needs more.
Report
You see what happened: a plain-English summary of every incident, plus regular threat reporting from our SOC.
What It Looks Like in Practice
Four things our SOC sees every week, and what happens next. Most are stopped automatically within seconds — and a person checks every one.
- Identity
Impossible travel
- We seeA sign-in from Irvine, then one from Lagos 20 minutes later on the same account.
- AutomaticallyEvery session on the account is signed out and a password reset is forced.
- Our SOCAn analyst confirms with the user and checks the mailbox for new forwarding rules or phishing sent from it.
- Location
Sign-in from outside the US
- We seeSomeone with the right password tries to sign in from a country you don’t do business in.
- AutomaticallyConditional access blocks it before it reaches email or files.
- Our SOCWe check with the user; if they really are travelling, we add a time-limited exception.
- Devices
Unusual movement on the network
- We seeOne PC suddenly reaches file shares and servers it has never touched, at 2 AM.
- AutomaticallySentinelOne isolates the device from the network, so nothing can spread.
- Our SOCAn analyst investigates, removes what caused it, rolls back changes if needed and reconnects the PC.
- Compliance
Out-of-date or unmanaged device
- We seeA laptop that’s missing updates — or a personal device — tries to open company email or files.
- AutomaticallyIntune marks it non-compliant and conditional access keeps company data off it.
- Our SOCThe user gets simple steps to fix it; we follow up until it’s compliant.
What’s Included in Our MxDR Service
Every component below is included in Managed Care, watched around the clock by our 24×7 NOC & SOC.
- Detect & respond
AI-driven detection and automated response
SentinelOne protects every managed endpoint, with real-time threat hunting and automated response that significantly reduce the risk of a breach.
SentinelOne - Visibility
Managed SIEM
Security log ingestion, analysis and storage from firewalls, Microsoft 365, Azure, AWS, Google Workspace, SentinelOne and other sources across your environment.
Log correlation - 24×7 people
24×7 Security Operations Center
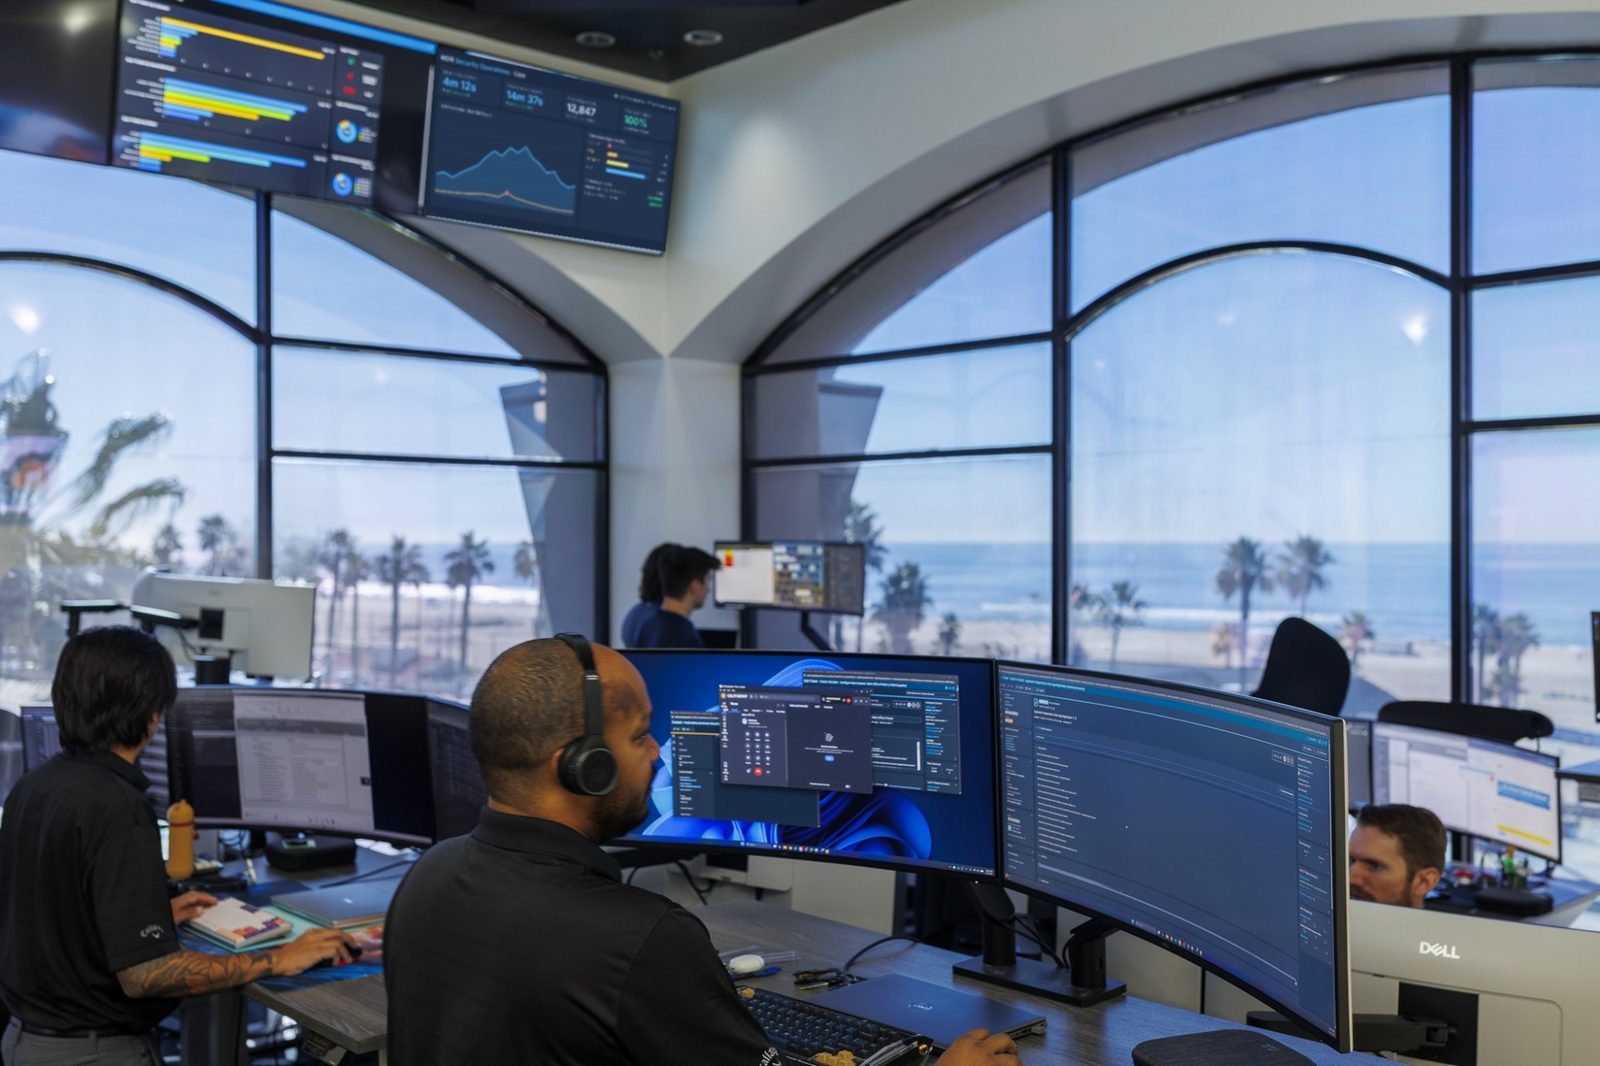
Security analysts monitor, investigate and respond to threats around the clock, alongside our 24×7 Network Operations Center (NOC).
SOC with NOC - Your access
Client access to SentinelOne
You get your own view of your environment’s protection and threats — full transparency, any time.
SentinelOne console
Protect your assets and reputation with MxDR services
CAL IT Group’s Managed Extended Detection and Response (MxDR) pairs SentinelOne with our 24×7 SOC. Every alert is investigated by a person, so real threats are contained quickly and false alarms don’t land on your staff. Operating around the clock, our team spots and deals with threats before they turn into outages or breaches.
Managed XDR, set up and watched for you
We believe that a robust cybersecurity strategy goes beyond the basics. Our goal is to give you detection and response that keeps up with the ever-evolving threat landscape — if you’re weighing it up, here’s what it adds beyond antivirus. We combine SentinelOne’s XDR platform with our own security expertise to offer a multi-layered defense that safeguards your organization’s digital assets.
Comprehensive detection and response
Our approach to detection and response is thorough and proactive. We understand that every second counts when it comes to mitigating threats, which is why we implement detection protocols that analyze data from various sources. This multi-vectored approach ensures that potential vulnerabilities are detected early, allowing for rapid and effective response.
Our detection strategies include real-time monitoring, behavioral analysis, and anomaly detection. By continuously examining your environment, we can identify unusual patterns and behaviors that might indicate a threat. Once detected, our rapid response protocols are set in motion, minimizing the potential impact of any malicious activity.
Incident investigation
When something gets through, knowing how it happened matters as much as cleaning it up. Our analysts use the SentinelOne and SIEM data already collected for your environment to work out the root cause, how far it spread and what data may have been exposed — and work alongside your insurer’s forensics firm when a claim is open.
An investigation covers:
Root cause
We identify the initial point of compromise and trace the steps taken by the attacker to gain access.
Scope
We determine the extent of the breach and identify any sensitive data that may have been compromised.
Evidence
We gather digital evidence, including logs and artifacts, to build a complete picture of the incident.
Malware
We look at the malware involved to understand what it did and whether anything else is affected.
Timeline
We reconstruct the sequence of events leading to the breach, helping you understand how the attack unfolded.
Recommendations
Based on our findings, we provide actionable recommendations to strengthen your security posture and prevent future incidents.
Explore our other cybersecurity solutions
We’re committed to providing holistic cybersecurity solutions that cover every aspect of your organization’s digital security. In addition to our Managed Extended Detection and Response (MxDR) Services, we offer a range of services, including ThreatLocker application allowlisting, compliance management, risk assessment, and vulnerability management. With our guidance, you can confidently navigate the complex IT landscape, knowing that your cybersecurity needs are well taken care of.