





Security Built Around Your People, Devices and Data
Businesses of all sizes must prioritize cybersecurity to protect their data, systems, and networks from malicious cyberattacks. Cybersecurity services provide an essential layer of protection for businesses, helping you secure networks, systems, and customer data. With the right strategies, you can be confident that your operations are secure.
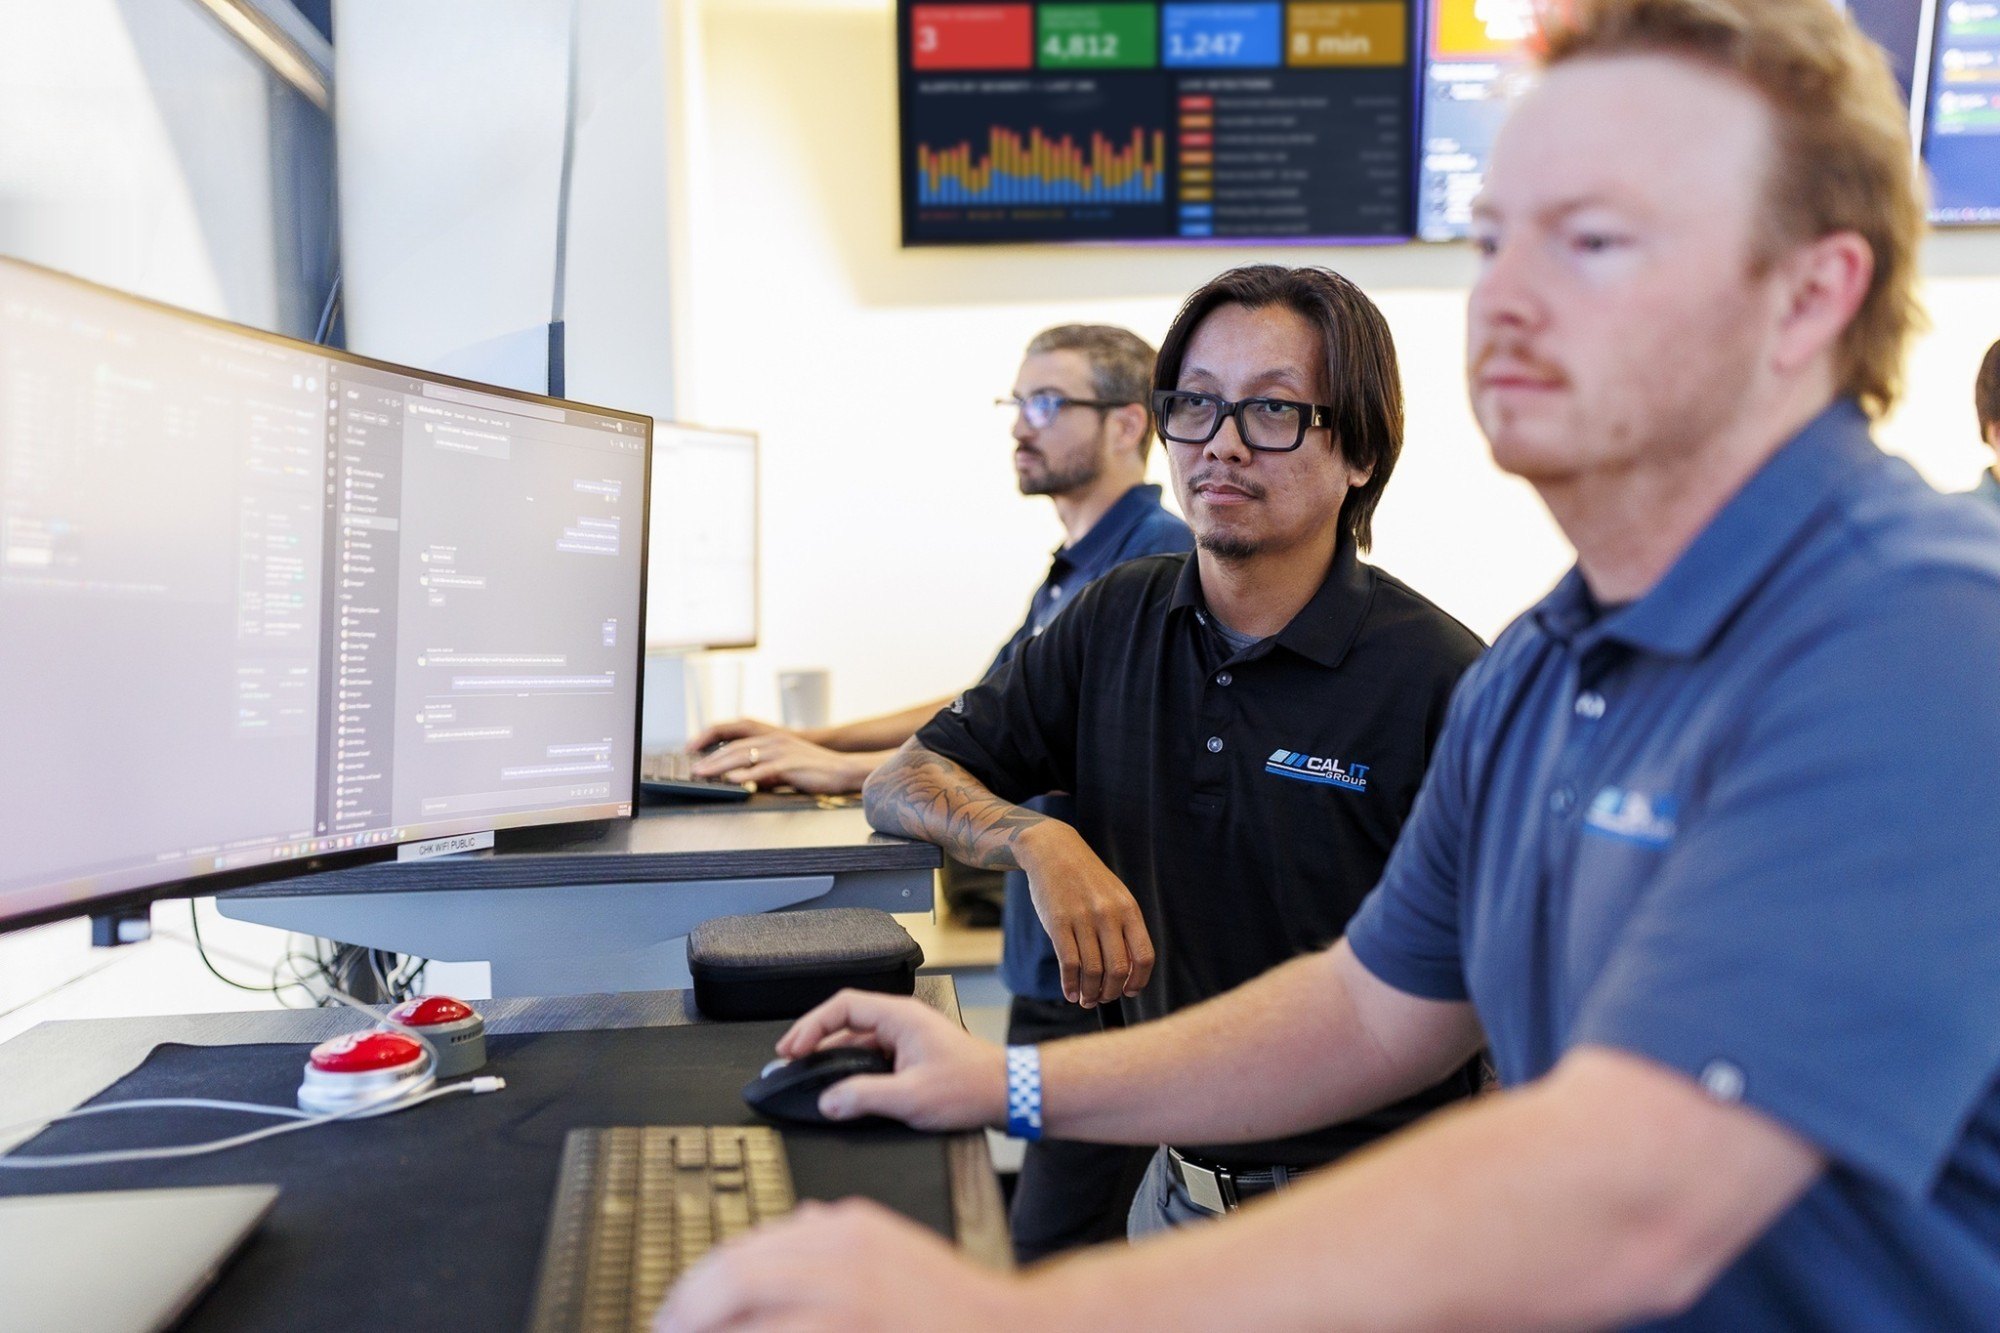
CAL IT Group provides managed cybersecurity for businesses across Orange County and Southern California. We build and run a complete security plan with you: security awareness training and phishing tests for your staff, endpoint protection and 24×7 monitoring for every device, and DNS filtering that blocks dangerous sites before they load.
We offer customized solutions tailored to the specific needs of each business so we can work with you to provide the best possible protection for your enterprise. No matter your core competencies, our team has the know-how and experience to ensure that your data and systems are safe from malicious actors. We proactively manage and monitor your security around the clock: patching, tuning and investigating every alert, so you can focus on running your business. Weighing the cost? Here’s how outsourcing security saves small businesses money.
The benefits of our advanced cybersecurity measures include:
Improved customer loyalty
Reduced risk of data breaches
Increased protection against unauthorized access
Increased productivity
Improved data integrity
The Full Security Stack — Included in Managed Care
Enterprise-grade cybersecurity for small and medium businesses, with no “security add-on” tiers. Every component below is included, and together they protect all four attack vectors: the human, devices, network and cloud.
- The human
Security awareness training
Online training plus simulated phishing campaigns, so every user can spot and report an attack.
Phishing simulations - The human
Multi-factor authentication
Deployed and managed for email and VPN access, stopping stolen passwords from opening the door.
Microsoft MFA - The human
Browser security
Remote browser isolation, advanced phishing defense and DNS filtering inside the browser — ideal for remote and hybrid teams.
DefensX - The human
Dark web monitoring
Alerts when your employees’ logins are leaked or for sale, with fast password resets by our team.
Credential alerts - Devices
Managed XDR & EDR
Next-generation antivirus, endpoint detection and response, and managed investigation on every managed endpoint.
SentinelOne - Devices
Device security & MDM
Hardened identity and device configuration, mobile device management and conditional access policies.¹
Microsoft Intune & Entra ID - Devices
Continuous vulnerability management
Internal and external scanning with remediation tracking, so gaps are closed before attackers find them.
Qualys - Network
24×7 Security Operations Center
Round-the-clock security monitoring, threat hunting and threat reporting, alongside our 24×7 Network Operations Center.
SOC with NOC - Network
Managed SIEM
Centralized collection and analysis of logs from firewalls, Microsoft 365, Google Workspace, Azure, AWS and SentinelOne.
Log correlation - Network
DNS content filtering
DNS-layer web filtering and threat blocking that stops connections to malicious sites.
Cisco Umbrella - Network
Attack surface management
Automated asset inventory, configuration change tracking and continuous misconfiguration detection.
Liongard - Cloud
Email security
Advanced protection against phishing, malicious links and attachments, and impersonation.¹
Microsoft Defender for Office 365 Plan 2 - Cloud
Microsoft 365 & Google Workspace backup
Backup and archive of email, files, calendars, contacts and chat.
Dropsuite - Strategy
vCISO services
Security strategy, compliance support and an annual cyber insurance review with your leadership.
Security leadership
¹ Requires the appropriate Microsoft licensing, billed separately.
Available at Additional Cost
- Add-on
ThreatLocker allowlisting
Zero-trust application control — only pre-approved applications can run, blocking malware and ransomware before it executes.
ThreatLocker - Add-on
Keeper Password Manager
Integration, management and support of Keeper so credentials are secure and available to the right people.
Keeper - Add-on
Annual penetration testing
A third-party test of your network, including a free retest. How it works
Third-party test - Add-on
Need something else?
Tell us what your insurer, customers or auditors are asking for, and we’ll scope it with you.
Talk to us
Not Sure Where You Stand? Start With an Assessment
The technology landscape constantly shifts, and keeping your footing can be a full-time commitment. CAL IT Group has the expertise and world-class solutions to relieve the pressure of your daily operations and give you the flexibility to pursue your goals stress-free.
Schedule My Network Health Assessment
How Each Layer of the Stack Works
Every layer below is part of the stack listed above, included in Managed Care and watched by our 24×7 Security Operations Center. Here is what each one does for your business, and how we run it.
Security Awareness Training
Most attacks start with a person, so we train yours. Every user gets short online training on phishing, social engineering, ransomware and safe habits.
We follow it with regular simulated phishing campaigns, track who clicks and who reports, and target extra training where it’s needed — so you can see your team getting harder to fool.
Multi-Factor Authentication
A stolen password shouldn’t be enough to get in. We deploy and manage Microsoft MFA for email, Microsoft 365 and VPN access.
We handle enrollment, lost phones and new hires, and review sign-in alerts, so MFA protects you without becoming a help desk headache.
Browser Security
The browser is where most work — and most attacks — happen. DefensX adds remote browser isolation, advanced phishing defense and DNS filtering inside the browser itself.
Because it travels with the user, remote and hybrid staff get the same protection at home, in a hotel or at a coffee shop as they do in the office. More on how to protect a remote or hybrid team.
Device Security, MDM & Conditional Access
With Microsoft Intune and Entra ID, we harden device and identity settings, manage laptops and mobile devices, and can wipe a lost or stolen device.
Conditional access policies decide who can reach your data and from where — for example, only from company-managed devices, or not from unexpected countries — so the right people get the right access at the right time.¹
Vulnerability Management & Patching
Qualys scans your network inside and out on a continuous schedule, and every finding is ranked by risk and tracked until it’s fixed.
Automated patching keeps Windows, macOS and common applications current, and we re-scan to prove each gap is closed.
24×7 Security Operations Center
Our SOC monitors your environment around the clock, alongside our 24×7 Network Operations Center — one team watching both security and uptime.
Alerts are investigated by people, not just logged. Analysts hunt for threats, contain what they find and report back to you in plain English.
Managed SIEM
Logs from your firewalls, Microsoft 365, Google Workspace, Azure, AWS and SentinelOne are collected in one place and correlated.
That lets our SOC spot attacks that only show up across several systems — like a suspicious sign-in followed by a mailbox rule change — and gives you an audit trail for compliance and cyber insurance.
DNS Content Filtering
Cisco Umbrella blocks connections to malicious, phishing and unwanted sites at the DNS layer — before a page or download ever loads.
It protects every device on your network, and we tune the categories to your business so it blocks threats without getting in the way of work.
Attack Surface Management
Liongard keeps an automated inventory of your systems and tracks configuration changes across firewalls, servers, Microsoft 365 and more.
When something changes that shouldn’t — a new admin account, a disabled security setting, an expiring certificate — we know about it and fix it.
Email Security
Microsoft Defender for Office 365 Plan 2 scans links and attachments, catches impersonation of your executives and vendors, and pulls malicious messages back out of inboxes after delivery.¹
We also set up and monitor SPF, DKIM and DMARC so criminals can’t send email as your domain. Check your domain free.
Microsoft 365 & Google Workspace Backup
Microsoft and Google keep their services running, but restoring your deleted or encrypted data is your responsibility. Dropsuite backs up and archives email, files, calendars, contacts and chat.
If a mailbox is deleted, a folder is wiped or ransomware reaches OneDrive, we restore it.
vCISO Services
Security leadership without a full-time hire. Your vCISO sets security strategy and priorities, supports compliance work and reviews your cyber insurance application with you each year.
You get a clear picture of where you stand, what’s next and why — in business terms, not jargon.
Endpoint protection: Managed XDR
Every managed laptop, desktop and server runs SentinelOne, monitored and investigated by our 24×7 SOC. It has its own page with the full details.
Secure Tomorrow Today
Prepare for the unexpected with CAL IT Group’s comprehensive backup and disaster recovery services. Our tailored solutions can secure your business continuity by ensuring your data and systems are always recoverable, no matter the disaster.