

5.0 on Google & Clutch 96%LIVE of calls answered in under 60 seconds by our local Huntington Beach team

vCISO Services for Orange County Businesses

Most growing companies need a security leader long before they can justify a full-time CISO. Our virtual CISO gives you one — a senior engineer who owns your security program, explains it in plain English and answers to your leadership team. It’s included in every Managed Care plan.

96%LIVE of calls answered in under 60 seconds by our local Huntington Beach team 24×7 NOC & SOC monitoring SOC 2 Type II all five Trust Services Criteria On-site support, included 5.0 on Google & Clutch

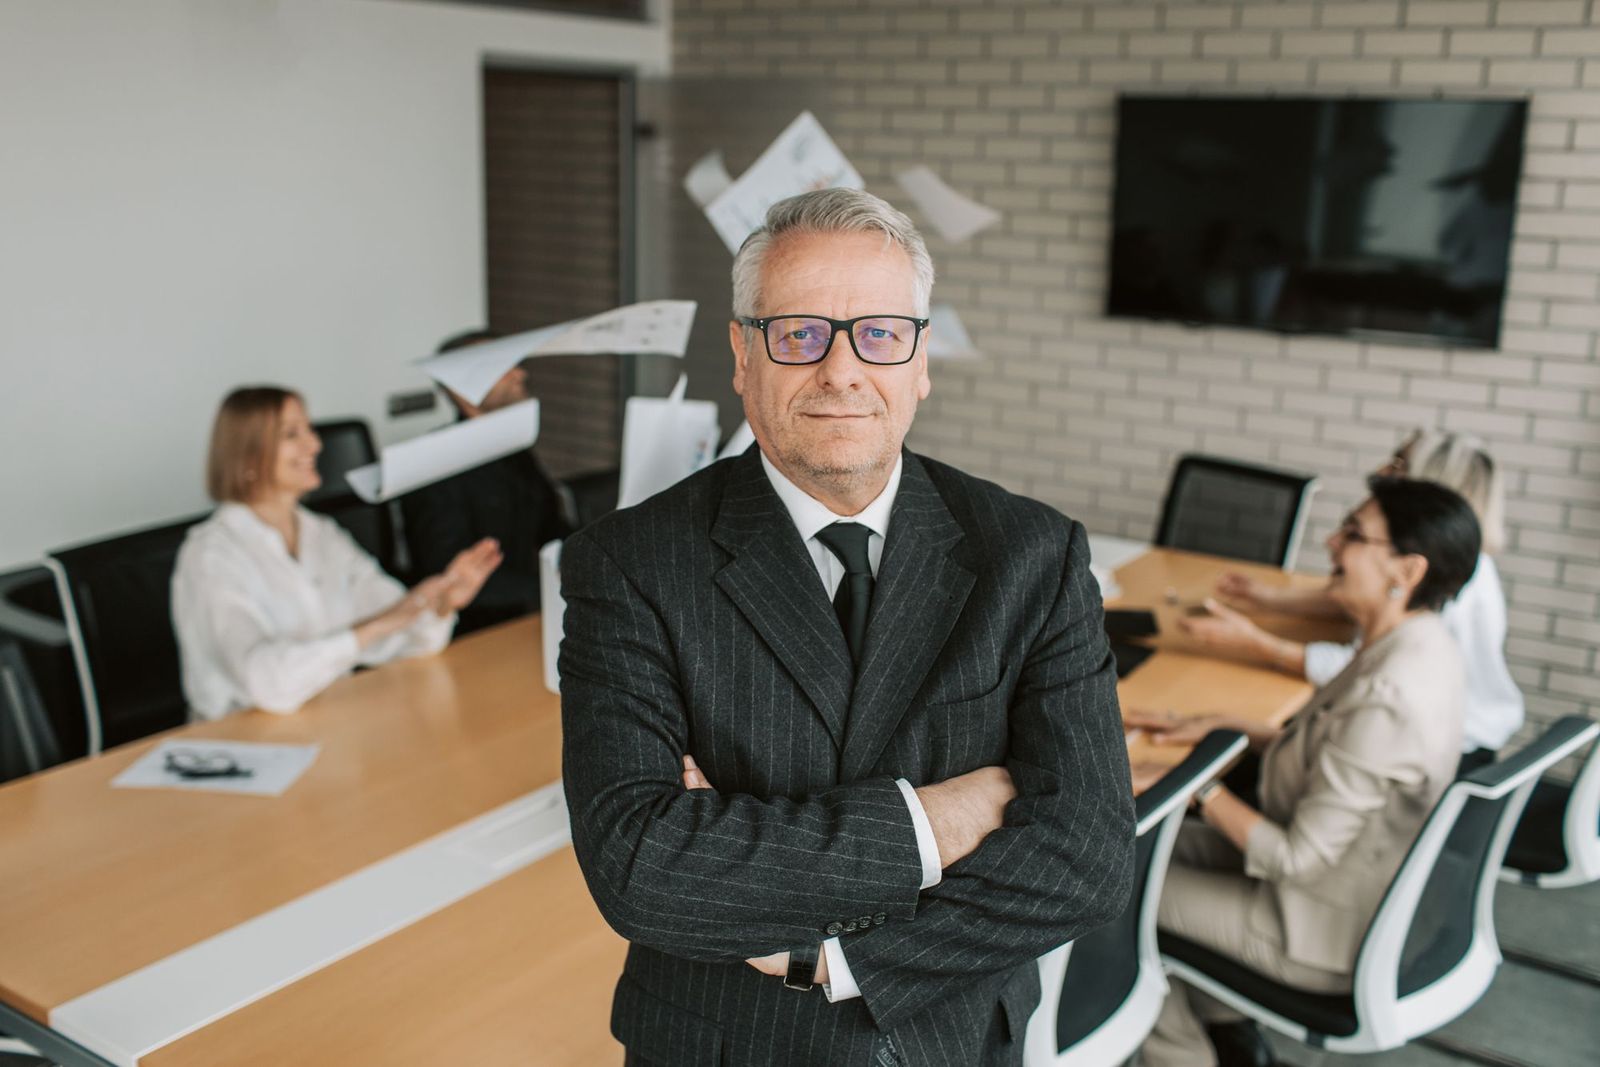
A senior executive standing in the boardroom while his team works behind him

vCISO · included in Managed Care

One person who owns your security program.

Your virtual CISO keeps the program moving: risks reviewed every quarter, policies people actually follow, insurance applications and customer questionnaires answered with evidence, and a plain-English report for leadership.

  • A security program built on the NIST Cybersecurity Framework
  • Quarterly risk reviews, with an owner and a due date for every fix
  • Insurance and customer questionnaires answered with proof
  • A one-page report for leadership at every quarterly review
Your security program, run by a virtual CISO A virtual CISO at the center of your security program: risks reviewed every quarter, written policies, insurance applications answered with evidence and a plain-English report for leadership. CISSP-led and included in Managed Care. Risk reviewsevery quarter Policiespeople actually follow Insuranceapplications answered Board reportin plain English vCISO NIST CSF program CISSP-led · in Managed Care Audit- and insurance-ready ✓

Technology partners

The platforms behind vCISO Services

See our partners →
  • Vanta logo
  • Microsoft logo
  • SentinelOne logo
  • Cisco Duo logo
  • Keeper Security logo

What your virtual CISO does

A security program is more than tools. Someone has to decide what matters most, write it down, check that it’s working and explain it to the people who sign the contracts. That’s the job of a CISO — and for most small and mid-sized businesses, a fractional one is the right size.

  • 01 · Program

    Security program and roadmap

    A written security program built on the NIST Cybersecurity Framework, with a prioritized roadmap and budget for the next 12 to 24 months.

    NIST CSF
  • 02 · Policies

    Policies people actually follow

    Acceptable use, access control, passwords and MFA, remote work, incident response and vendor management — written for how your company works, not copied from a template.

    Policy set
  • 03 · Risk

    Risk register and reviews

    Your top risks ranked by impact and likelihood, reviewed with you every quarter, with an owner and a due date for every fix.

    Quarterly review
  • 04 · Compliance

    Compliance mapped and evidenced

    Controls mapped to the frameworks you answer to — CMMC and NIST 800-171, SOC 2 or PCI DSS — with the evidence kept on file.

    Control map
  • 05 · Questionnaires

    Customer and insurance questions

    We answer security questionnaires from your customers and the security sections of your cyber insurance application, with proof behind every answer.

    Evidence on file
  • 06 · Incidents

    Incident response plan and drill

    A short, practical plan with names, numbers and first steps, and a tabletop exercise with your leadership once a year.

    Tabletop exercise
  • 07 · Vendors

    Third-party risk

    A review of the vendors and apps that hold your data or reach into your network, and what you should ask them for.

    Vendor review
  • 08 · Report

    A plain-English report for leadership

    Where you stand, what changed, what’s next and what it costs — on one page, at every quarterly business review.

    One-page report

Included in Managed Care, not billed by the hour

Every Managed Care plan includes vCIO and vCISO services, along with the security your vCISO reports on: SentinelOne MxDR and EDR, a 24×7 NOC & SOC, managed SIEM, vulnerability management, email security, DNS filtering, security awareness training and MFA. Your vCISO isn’t an outside consultant guessing at your environment — they work with the same engineers who support you every day. See what’s included on our pricing page.

Who needs a vCISO

You’re answering security questionnaires

Customers, especially larger ones, now send long security questionnaires before they sign or renew. We answer them accurately and fix what they uncover.

You’re working toward CMMC

Defense suppliers need a System Security Plan, a POA&M and someone to own them. See our CMMC compliance services and the free CMMC score estimator.

Your cyber insurance renewal is coming

Insurers ask detailed questions about MFA, backups, EDR and training. Try the cyber insurance readiness check before your broker sends the application.

Customers are asking for SOC 2

A vCISO keeps the program running between audits. See SOC 2 readiness.

Why CAL IT Group

  • We hold SOC 2 Type II across all five Trust Services Criteria — we run our own security program to the standard we help you meet
  • Highly technical leadership — co-founders Kevin Nichols and Joe Kemp, a CISSP — with 55+ years of combined IT experience
  • A local team in Huntington Beach, with on-site support included in Managed Care
  • One team for leadership and hands-on work: the people who write your plan are the people who carry it out

Talk to us about a vCISO Take the cyber risk self-check

What sets us apart

Fast response, deep security, senior expertise and engineers on-site.

<60 sec to a live engineer

Response time you can measure

96%LIVE of calls are answered by an engineer in under 60 seconds, every ticket is assigned in under 10 minutes, and every email or portal ticket gets a real engineer within 20 minutes (Mon–Fri, 5 AM–6 PM). Calls never go to voicemail during service desk hours, and the same team is on call 24×7.

See the live numbers →

24×7 NOC & SOC MSSP-grade security

A security provider, not just an IT provider

We operate as a managed security service provider (MSSP): SentinelOne MxDR, a 24×7 NOC & SOC, managed SIEM, DefensX browser security, security awareness training, vulnerability management, penetration testing and CMMC support — run by a team audited for SOC 2 Type II across all five Trust Services Criteria.

Our security services →

55+ years of combined experience

Senior technical expertise behind every ticket

Led by hands-on co-founders Kevin Nichols and Joe Kemp, with 55+ years of combined IT experience. Every engineer passes a technical assessment, we staff above our workload, and nobody works on something they’ve never seen before without an experienced engineer alongside — no call center, no offshore tier.

Meet the founders →

On-site included, no trip fees

Engineers who come to you

When hands-on work is needed, a local engineer is dispatched from our Huntington Beach office. On-site support is included in Managed Care — no dispatch fees, trip charges or hourly on-site rates — from the same team that knows your environment.

Areas we serve →

We re-earn your business on every ticket. No contract ever replaces doing the work well. Every user who opens a ticket gets a satisfaction survey when it closes, and every score is visible to our whole team and leadership — the averages are published live for anyone to see.

See our survey results →

Best-of-breed, by design

Industry-leading tools, chosen and run by engineers

We’re technology agnostic: we don’t resell a single vendor’s bundle or push the platform with the best margin. Every tool we recommend is a best-of-breed industry leader — selected, tested and configured by our own engineers because it’s right for your business.

Our leadership team is highly technical. Our co-founders, Kevin Nichols and Joe Kemp, are hands-on engineers, not just managers, and they constantly re-evaluate our tools and service offering — retiring what falls behind and adding what keeps clients ahead. You get enterprise-class technology that keeps improving, without lifting a finger.

  • SentinelOneMxDR endpoint protection
  • Microsoft DefenderPlan 2 & Intune device management
  • QualysVulnerability management
  • LiongardConfiguration & change monitoring
  • NinjaOneRemote monitoring & patching
  • 24×7 NOC & SOCManaged SIEM & threat hunting
  • Veeam + AzureBackup & off-site replication
  • Azure Site RecoveryCloud disaster recovery

Just some of the technologies we use.

vCISO Services FAQs

What does a vCISO do?

A virtual Chief Information Security Officer owns your security program: sets the policies, keeps a risk register, tracks the fixes, answers customer security questionnaires and insurance applications, and reports progress to your leadership. It’s a leadership role, backed by the engineers who run your security day to day.

Is vCISO included in Managed Care?

Yes. vCIO and vCISO services are part of every Managed Care plan at no extra charge. Third-party audits and certifications (for example a SOC 2 or CMMC assessment) are performed and billed by the auditor; we prepare you for them.

How is a vCISO different from a vCIO?

The vCIO plans your technology — roadmap, budget and vendors. The vCISO plans your security — risks, controls, policies and compliance. With Managed Care you get both, working from the same quarterly business review.

Can a vCISO help with our cyber insurance renewal?

Yes. We complete the security sections of your application with you, collect the evidence for each control and close the gaps before renewal. Our free cyber insurance readiness check shows where you stand today.

Do you work alongside our own IT staff?

Yes. With co-managed IT, your team keeps day-to-day support and we add security leadership, our 24×7 SOC and the security stack.

Success stories

Rated 5.0 on Google and Clutch.

Real reviews from the businesses we support — not a curated quote wall.

★★★★★Google
“Knowledgeable and proactive group that partners with you to assure your objectives are met, along with planning for future needs. All balanced with supporting your business day in and day out with a friendly, responsive and competent help desk. Recommend and would select them again!”
Tom G
★★★★★Google
“CAL IT has been a game changer for us. They tackle issues quickly and efficiently for us. So grateful their expertise. I highly recommend their services.”
Kelli Foudy
★★★★★Google
“We have worked with Cal It for several years now, They are very responsive and professional. We would highly recommend them.”
Cathy Goff

Customer service first · we re-earn your business on every ticket

Obsessive about service. Relentless about the details.

CAL IT Group brings enterprise-class IT, cybersecurity and SOC 2 Type II–audited operational excellence to small and midsize businesses across Southern California — a customer service organization first and foremost, proven day in and day out for over 10 years.

Call 866.24.CALIT